﻿# ASP.NET 發現重大資安弱點影響範圍涵蓋 ASP.NET 1.0 ~ 4.0

幾天前有兩位資安研究員 ([Thai Duong](https://x.com/thaidn) and [Juliano Rizzo](https://x.com/julianor)) 發現了一個 ASP.NET 的資安弱點，主要的點出在 .NET 實做 AES 加解密演算法的問題，駭客透過這個弱點即可在短時間內猜出你網站的加密金鑰進而入侵你的網站系統，在 ASP.NET 裡使用到加解密的地方非常多，像是 [Forms Authentication](/post/2008/02/20/Explain-Forms-Authentication-in-ASPNET-20) 與 ViewState 都是非常常見的功能，加密金鑰 (MachineKey) 被猜到之後就可以讓駭客用任意身份使用你的網站或任意竄改 ViewState 中的狀態資訊，嚴重性非同小可，各位一定要即時因應。

**!!! 注意：此資安弱點微軟已經釋出更新，請當下立即執行 Windows Update 更新系統！**

由於這是 AES 演算法實做的問題，不僅僅是 ASP.NET 受害，連 Java 陣營的人也一樣逃不掉，該研究員宣稱他們僅需花費 30 到 50 分鐘的時間就能 100% 破解任意用 AES 加解密的網站，他們還撰寫了一個名為 [POET ( Padding Oracle Exploit Tool )](https://github.com/jaideepjha/POET) 的工具可供下載驗證，甚至還有人錄製完整的破解過程並放上 YouTube，有興趣的人可以看看以下 YouTube 影片：

-   \[ .NET \]  [POET vs ASP.NET: DotNetNuke](http://www.youtube.com/watch?v=yghiC_U2RaM)

<object width="425" height="355"><param name="movie" value="http://www.youtube.com/v/yghiC_U2RaM?fs=1&amp;hl=zh_TW&amp;hl=en"><embed src="http://www.youtube.com/v/yghiC_U2RaM?fs=1&amp;hl=zh_TW&amp;hl=en" type="application/x-shockwave-flash" width="425" height="355"></object>

-   \[ Java \]  [Padding Oracle Exploit Tool vs Apache MyFaces](http://www.youtube.com/watch?v=euujmKDxmC4)

<object width="425" height="355"><param name="movie" value="http://www.youtube.com/v/euujmKDxmC4?fs=1&amp;hl=zh_TW&amp;hl=en"><embed src="http://www.youtube.com/v/euujmKDxmC4?fs=1&amp;hl=zh_TW&amp;hl=en" type="application/x-shockwave-flash" width="425" height="355"></object>

在 ASP.NET 的世界裡，使用 [Forms Authentication](/post/2008/02/20/Explain-Forms-Authentication-in-ASPNET-20) 的網站多如牛毛，若是 MachineKey 被取得，影響層面之廣難以估計，你可能會以為儲存在 userData 裡面的資料都可以完整被保護，因此有許多網站會將角色權限的資訊通通儲存在這裡，當網站被破解後，就可以讓攻擊者任意寫入 userData 的內容，攻擊者甚至可以直接用管理者的身份或權限操作你的網站前台或後台管理介面。

但為什麼這次從 ASP.NET 1.0 到 ASP.NET 4.0 全軍覆沒呢？！因為打從一開始的 ASP.NET 1.0 其加解密演算法都是以 **Auto** 為預設值，我們可以依據《[如何快速查詢 web.config 中各項設定參數的預設值](/post/2009/06/19/check-webconfig-default-settings-and-options-with-ease.aspx)》所提到的技巧即可發現系統的預設值為何：

![alt](https://stwillblogassets.blob.core.windows.net/files/images/external/stwillblogassets.blob.core.windows.net/3834c65c7c54478cd8d7-image_205.png "title")

而我在 MSDN 的 [How To Configure MachineKey in ASP.NET 2](http://msdn.microsoft.com/en-us/library/ff649308.aspx) 文件也看到 Auto 預設的就是使用 AES 演算法：

![alt](https://stwillblogassets.blob.core.windows.net/files/images/external/stwillblogassets.blob.core.windows.net/5add3dcd1233d67f0d43-image_206.png "title")

**〈注意〉**即便你手動修改 web.config 將演算法切換至 3DES 也不會減緩這次的問題，因為 3DES 與 AES 演算法的實做都是共用相同的 cryptographic padding mode ([CBC](http://en.wikipedia.org/wiki/Block_cipher_modes_of_operation#Cipher-block_chaining_.28CBC.29))，所以一樣會輕易破功！而 DES 基本上與 3DES 只有金鑰長度不一樣而已，而且 DES 演算法的強度不夠 (金鑰不夠長)，所以也是不建議切換到 DES 加密模式。

這問題在 2 天前微軟也正式公布了 [Microsoft Security Advisory (2416728) - Vulnerability in ASP.NET Could Allow Information Disclosure](https://learn.microsoft.com/en-us/security-updates/securityadvisories/2010/2416728) 這個弱點，不過目前尚未有完整的解決方法，僅有短期的 **應變措施** (Workaround)，建議各位 IT 人員儘速利用文件所述的 Workaround 說明進行網站修正。

這次的弱點若被攻陷，問題損害的不僅僅是讓駭客任意操作 [Forms Authentication](/post/2008/02/20/Explain-Forms-Authentication-in-ASPNET-20) 與 ViewState 而已，如果你使用的 **ASP.NET 3.5 SP1 以上的版本**，甚至可以利用這次的弱點取得你網站主機上的任意檔案 ( 例如 web.config )，任何 Worker Proccess 有權限存取的檔案都可以被任意取回。詳細說明請參考 [Understanding the ASP.NET Vulnerability](http://blogs.technet.com/b/srd/archive/2010/09/17/understanding-the-asp-net-vulnerability.aspx) ( 註：此文章並沒有提及如何驗證可被下載檔案的步驟，這部分我也無法驗證是否真的這種狀況，不過基本上由微軟官方發佈的消息來看，可信度相當高！ )

昨天 [ScottGu](http://weblogs.asp.net/scottgu/) 也在部落格上發佈[這個消息](https://weblogs.asp.net/scottgu/important-asp-net-security-vulnerability) ( [Important: ASP.NET Security Vulnerability](https://weblogs.asp.net/scottgu/important-asp-net-security-vulnerability) )，目前來說最快速可實施的應變措施就是修改 web.config 的設定值，讓攻擊者無法透過網站回應預設 ASP.NET 的錯誤訊息來進一步猜出 MachineKey 是多少，以下便是這次應變措施的修改步驟：

1.  開啟 web.config 設定檔
2.  在 <customErrors> 設定的地方設定好 mode 與 defaultRedirect 屬性 ( **注意: 兩個屬性都要設定** )
    
    ```
    <customErrors mode="On" defaultRedirect="~/error.aspx" />
    ```
    
    如果是 **ASP.NET 3.5 SP1** 或 **ASP.NET 4.0** 的話，設定格式如下：
    
    ```
    <customErrors mode="On" redirectMode="ResponseRewrite" defaultRedirect="~/error.aspx" />
    ```
    
    **注意**：請不用使用以下這種有設定 <error> 的設定法，這還是容易讓駭客猜出你的錯誤類型！因為 POET 會利用你 ASP.NET 所回傳的 HTTP Status Code 來判斷猜測成功或失敗！

```
<customErrors mode="On" redirectMode="ResponseRewrite">  <error statusCode="404" redirect="~/404.aspx"/>  <error statusCode="500" redirect="~/error.aspx"/></customErrors>
```

4.  新增一個專用的 **error.aspx** 錯誤結果頁面，其程式碼內容參考如下：

```csharp
<%@ Page Language="C#" AutoEventWireup="true" %>
<%@ Import Namespace="System.Security.Cryptography" %>
<%@ Import Namespace="System.Threading" %>

<script runat="server">
   void Page_Load() {
      byte[] delay = new byte[1];
      RandomNumberGenerator prng = new RNGCryptoServiceProvider();

      prng.GetBytes(delay);
      Thread.Sleep((int)delay[0]);
        
      IDisposable disposable = prng as IDisposable;
      if (disposable != null) { disposable.Dispose(); }
    }
</script>

<html>
<head runat="server">
    <title>Error</title>
</head>
<body>
    <div>
        An error occurred while processing your request.
    </div>
</body>
</html>
```

**〈注意〉此攻擊手法並非透過判斷「錯誤訊息內容」來猜出金鑰，只要網站回應了錯誤(或非預期)的訊息就可以判定為猜錯了，進而再次猜測下一個組合。增加 Thread.Sleep 的時間只能延緩網站被攻破的時間，不能保證網站就此高枕無憂。**

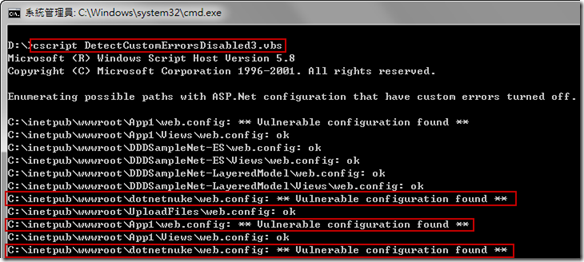
最後，ASP.NET 開發團隊也釋出了一個[偵測 <customError> 是否被停用的 VBScript 程式](http://www.asp.net/media/782788/detectcustomerrorsdisabledv30.zip "published a .vbs script")，該程式下載後直接執行就會自動開始對你的 IIS 進行分析，他會把註冊在 IIS 中的所有 Web 應用程式的 web.config 開啟並檢查是否做到上述的設定步驟，如果看到下圖執行結果標紅框的部分就代表的你的網站正處於極度危險的狀態！ ( 點圖可放大顯示 )

[![alt](https://stwillblogassets.blob.core.windows.net/files/images/external/stwillblogassets.blob.core.windows.net/728a033d311c7a4cdf85-image_thumb_29.png "title")](https://stwillblogassets.blob.core.windows.net/files/images/external/stwillblogassets.blob.core.windows.net/322887218ab0acaa26ba-image_207.png)

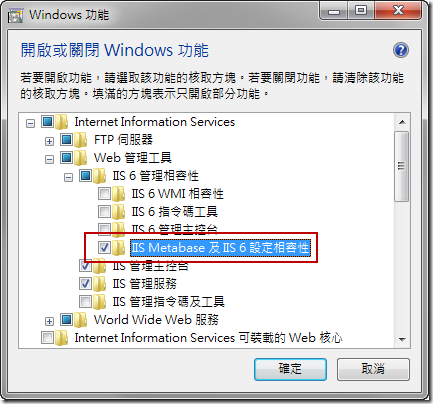
**注意**：若要在 IIS7 下執行此程式，必須先安裝 **IIS Metabase 及  IIS 6 設定相容性** 功能
![alt](https://stwillblogassets.blob.core.windows.net/files/images/external/stwillblogassets.blob.core.windows.net/80be1a765c01138247d5-image_208.png "title")

我怕有人不知道 ASP.NET 技術是否包括 ASP.NET MVC，所以特別再額外提醒一點，我這裡講的 ASP.NET 資安弱點，影響的範圍包括 ASP.NET MVC、SharePoint、ReportServer、TFS Team Web Access、Microsoft CRM、Microsoft Exchange Web Access 以及任何以 ASP.NET 技術為基礎的網站都會遭受此弱點的攻擊喔！

另外，如果你的網站是以 Web Farm 架構在運行，記得所有主機上的 web.config 都要一併修改喔！

**相關連結**

-   [Security Hack Exposes Forms Authentication in ASP.NET](http://visualstudiomagazine.com/articles/2010/09/14/aspnet-security-hack.aspx)
-   [Security researchers 'destroy' Microsoft ASP.NET security](http://www.theinquirer.net/inquirer/news/1732956/security-researchers-destroy-microsoft-aspnet-security) \[ [Discussion](http://news.ycombinator.com/item?id=1701502) \]
-   [Fear, uncertainty and and the padding oracle exploit in ASP.NET](http://www.troyhunt.com/2010/09/fear-uncertainty-and-and-padding-oracle.html)
-   ['Padding Oracle' Crypto Attack Affects Millions of ASP.NET Apps](http://threatpost.com/en_us/blogs/new-crypto-attack-affects-millions-aspnet-apps-091310)
-   [Security Vulnerability in ASP .Net — Padding Oracle Attack](https://web.archive.org/web/20130617133501/http://leonardwoody.com/2010/09/18/security-vulnerability-in-asp-net/)
-   [Padding Oracle Exploit Tool ( POET )](https://github.com/jaideepjha/POET)
-   [Juliano Rizzo (julianor) on Twitter](https://x.com/julianor)
-   [Padding oracles everywhere](https://web.archive.org/web/20150415160534/http://ekoparty.org/juliano-rizzo-2010.php)
-   [Details about ASP.NET Security Vulnerability](https://web.archive.org/web/20140123043252/http://abdullin.com:80/journal/2010/9/19/details-about-aspnet-security-vulnerability.html)
-   [Automated Padding Oracle Attacks with PadBuster](http://www.gdssecurity.com/l/b/2010/09/14/automated-padding-oracle-attacks-with-padbuster/)
-   [CVE-2010-3332](https://www.cve.org/CVERecord?id=CVE-2010-3332)
-   !!! [Microsoft Security Bulletin MS10-070 – Important](https://learn.microsoft.com/en-us/security-updates/securitybulletins/2010/ms10-070)  
        - Vulnerability in ASP.NET Could Allow Information Disclosure (2418042)
-   [Microsoft Security Advisory (2416728)](https://learn.microsoft.com/en-us/security-updates/securityadvisories/2010/2416728)  
        - Vulnerability in ASP.NET Could Allow Information Disclosure
-   !!! [Important: ASP.NET Security Vulnerability - ScottGu's Blog](https://weblogs.asp.net/scottgu/important-asp-net-security-vulnerability)
-   !!! [Frequently Asked Questions about the ASP.NET Security Vulnerability - ScottGu's Blog](https://weblogs.asp.net/scottgu/frequently-asked-questions-about-the-asp-net-security-vulnerability)
-   !!! [Update on ASP.NET Vulnerability](https://weblogs.asp.net/scottgu/update-on-asp-net-vulnerability)
-   !!! [ASP.NET Security Update Now Available](https://weblogs.asp.net/scottgu/asp-net-security-update-now-available)
-   !!! [ASP.NET Security Fix Now on Windows Update](https://weblogs.asp.net/scottgu/asp-net-security-fix-now-on-windows-update)
-   [Understanding the ASP.NET Vulnerability](http://blogs.technet.com/b/srd/archive/2010/09/17/understanding-the-asp-net-vulnerability.aspx)
-   [ASP.NET Forums » General ASP.NET » Security Vulnerability](http://forums.asp.net/1233.aspx)
-   [How To Configure MachineKey in ASP.NET 2](http://msdn.microsoft.com/en-us/library/ff649308.aspx)
-   [machineKey Element (ASP.NET Settings Schema)](http://msdn.microsoft.com/en-us/library/w8h3skw9.aspx)
-   [ASP.NET Security Vulnerability workaround for DotNetNuke sites](http://www.dotnetnuke.com/Community/Blogs/tabid/825/EntryId/2798/ASP-NET-Security-Vulnerability-workaround-for-DotNetNuke-sites.aspx)
-   [Block cipher modes of operation](http://en.wikipedia.org/wiki/Block_cipher_modes_of_operation)
-   ASP.NET POET Vulnerability - What Else Can I Do?
-   [【重要提醒】請全面檢視並修改web.config customErrors!](http://blog.darkthread.net/blogs/darkthreadtw/archive/2010/09/19/fix-customerrors-now.aspx)
-   [\[ASP.NET\] ASP.NET 零時差攻擊 – POET 原理與防禦措施](https://dotblogs.com.tw/regionbbs/2010/09/21/asp_net_poet_security_vulnerability)